Customer.io opens the full Design Studio lifecycle to its API
Programmatic email work can now move from supplied HTML through review and testing into a linked workflow and later publication. The operational opportunity is a governed release path, not faster sends alone.
What Customer.io released
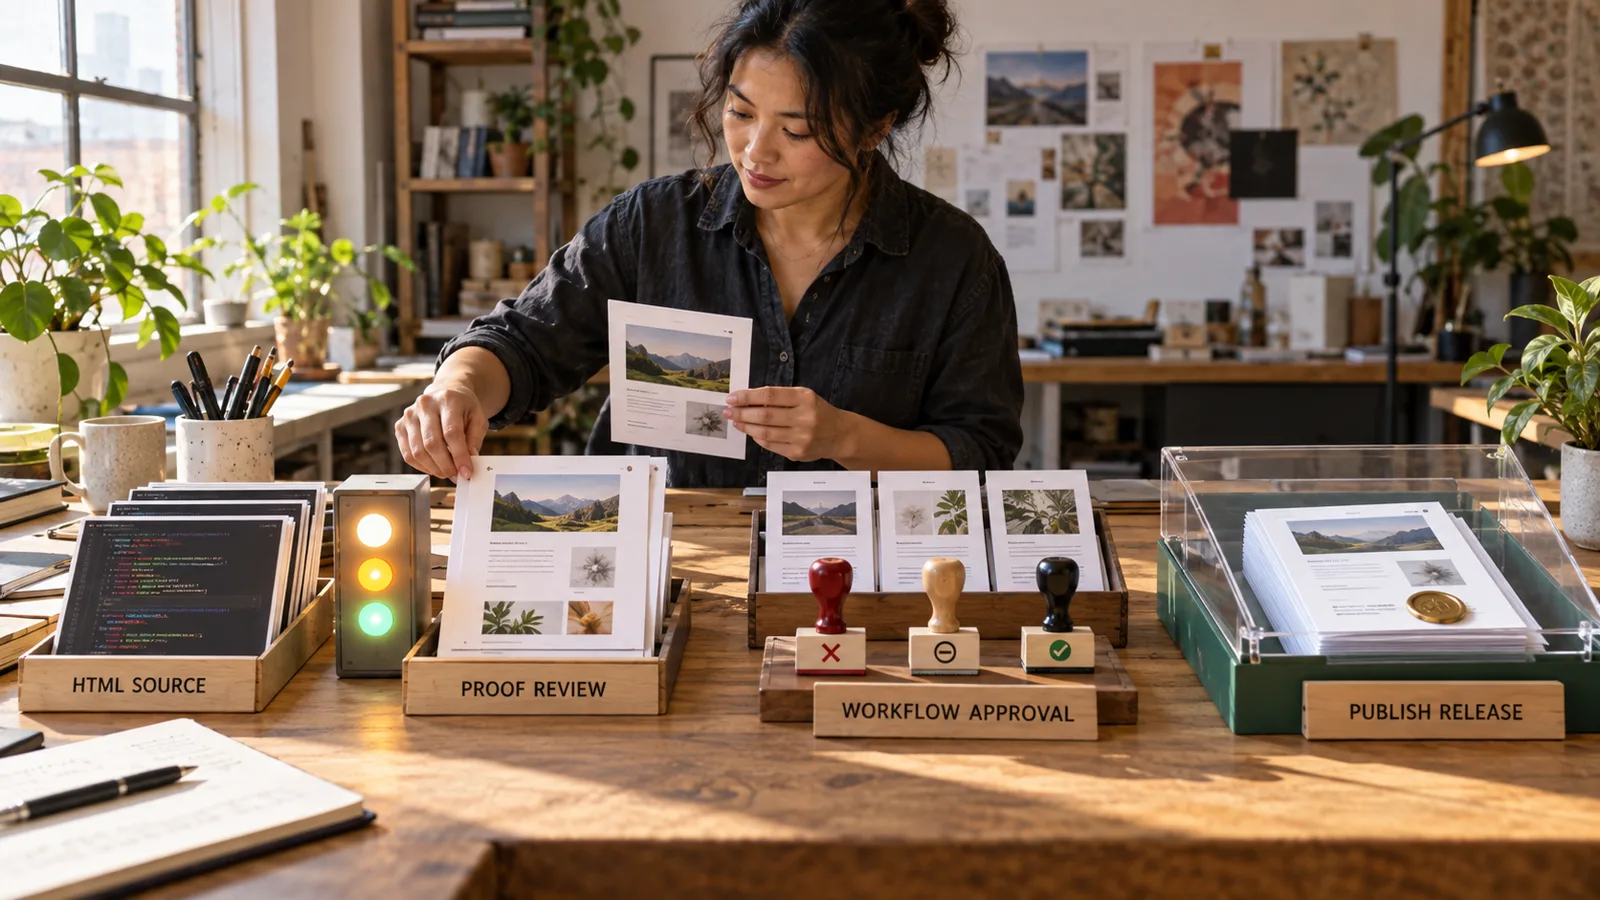
Customer.io's official release notes dated October 6 describe an expanded Design Studio API that can take an email through its full lifecycle. An operator or application can create content from supplied HTML, review and test it, link it to a workflow and publish later changes. Customer.io presents those as separate stages rather than one opaque send operation.
That distinction is the material RevOps signal. A team can keep its content source, review process and automation outside the visual editor while still using Customer.io as the controlled destination. It also means a failed or incomplete API sequence can leave a valid asset in the wrong state. Creation, attachment and publication must therefore be reconciled independently.
- Confirm the API capability and scopes in the target workspace.
- Record the content ID, workflow ID and environment.
- Treat source release date separately from DailyRevOps publication date.
Sources: Customer.io release notes
A content object is not a released journey
An email created from HTML may exist successfully while still being unattached, attached to the wrong workflow or unpublished. RevOps should expose those states in the release record instead of translating every successful API response into campaign ready. The minimum state model is source accepted, render reviewed, tests passed, workflow link verified, publish approved and destination read back.
Keep stable identifiers from the first step. A title is convenient for people but weak for reconciliation when several versions share a name. Store the content ID, workspace, workflow ID, version, source revision and expected publication state. After any retry, query those identifiers before creating a replacement so the recovery path does not multiply content objects.
- Use stable IDs rather than titles for reconciliation.
- Make every intermediate state visible.
- Design retries to resume instead of duplicate.
Review and test need explicit acceptance criteria
The release note says the API supports review and testing, but it does not define a universal quality bar for every customer. Teams must supply that contract. Check approved sender identity, subject and preheader, required legal text, links, tracking parameters, personalization fallbacks, plain-text behavior and a representative set of rendering environments.
A test delivery proves that a message can be generated and delivered to the test target. It does not prove that production segmentation, consent, suppression, frequency caps or workflow timing are correct. Keep content QA and audience QA as different gates with different evidence and owners.
- Separate render tests from audience tests.
- Require an owner for legal and brand rules.
- Preserve the accepted preview and test result.
Workflow linking creates a second authority boundary
Once content is linked to a workflow, the release inherits the workflow's entry rules, delays, branching and exit behavior. Content approval does not approve that surrounding automation. A reviewer should see the exact workflow and step that will reference the content, plus whether the workflow is active, scheduled or still in preparation.
Use a preflight population with known edge cases: a fully eligible person, a suppressed person, missing personalization data, conflicting consent, an account in another region and a recently changed subscription state. The intended result for each case should be written before execution. That makes the test useful when a safe rejection is the correct outcome.
- Read the workflow link after writing it.
- Test positive and negative audience cases.
- Do not infer consent from content approval.
Publication should produce a receipt
A publish call is consequential because later workflow activity may reach customers without another editor session. The release receipt should name the actor or service identity, source revision, content and workflow IDs, approval, publication time and destination state. It should also include a rollback target and the condition that triggers rollback.
Do not close the release on a 2xx response alone. Fetch the destination after publication and compare the fields that matter: version, status, workflow association and any server-generated values. For asynchronous processing, retain the acknowledgement but keep the release open until the authoritative state is visible or the exception owner accepts the unresolved result.
- Require a named approval before publish.
- Read back the final destination state.
- Keep a tested rollback target.
Changes after launch need the same discipline
The release notes explicitly mention publishing changes later. Post-launch edits are not a lesser form of release. A small copy change can alter a promise, remove required language, break a link or invalidate a reviewed rendering. Tie each change to a source revision and repeat the relevant checks rather than carrying forward a blanket approval.
Where possible, use a bounded canary or controlled internal audience before the full eligible population. If Customer.io applies an update to content already referenced by an active workflow, record which future deliveries receive the new version and how in-flight records are treated. If that behavior is not documented for the target configuration, verify it safely rather than guessing.
- Version every post-launch change.
- Define treatment of in-flight records.
- Repeat checks affected by the edit.
Measure release quality, not API volume
The number of API-created emails says little about operating quality. Better local measures include releases passing without rework, median time from approved source to verified publication, duplicate-content incidents, unresolved link mismatches, rollback time and the share of sends attributable to a retained release receipt.
Publish denominators and exclusions. If 19 of 20 releases passed, name the 20 eligible releases and explain the failure. Do not convert a local process measure into a claim about Customer.io's platform performance. The API creates the control points; the customer defines and operates them.
- Count eligible releases before calculating rates.
- Track duplicates and unresolved states.
- Separate local performance from vendor claims.
The operator takeaway
Customer.io's Design Studio API expansion is useful because it exposes a programmatic path across the content lifecycle, not merely an endpoint that pushes HTML. It can connect a source-controlled production system to a lifecycle platform while preserving review, testing and publication as explicit steps.
The win depends on keeping those steps distinct. Give content, workflow and audience their own authority checks; retain stable IDs; verify the destination after consequential writes; and close every release with evidence and recovery. That turns automation into a reviewable operating path instead of a faster route to an unverified send.
- Pilot one workflow with a frozen cohort.
- Require evidence for every state transition.
- Expand only after recovery is proven.
Original source
This DailyRevOps article is written in our own words from the source signal and adds RevOps context, workflow analysis, and operator interpretation.
- Original source: Customer.io
- Original publication date:
- Source link: Read the original article
Customer.io dated the release October 6, 2026; DailyRevOps first published this operator analysis October 11, 2026.